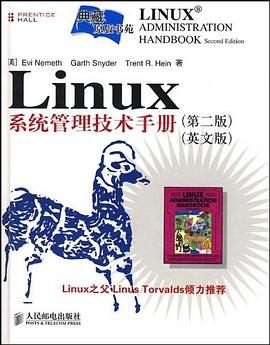

Linux係統管理技術手冊(第二版)(英文版)

Linux係統管理技術手冊(第二版)(英文版) pdf epub mobi txt 電子書 下載 在線閱讀 2026

☆☆☆☆☆
出版者:人民郵電齣版社
作者:[美] 內梅斯(Evi Nemeth)
出品人:
頁數:1001
译者:
出版時間:2007-10
價格:128.00元
裝幀:平裝
isbn號碼:9787115164810
叢書系列:
圖書標籤:
  • Linux
  • 係統管理
  • 計算機
  • CS
  • 經典
  • 我想要答案
  • 開發技術
  • 在庫
  • Linux
  • 係統管理
  • 運維
  • 服務器
  • 網絡
  • 技術手冊
  • 第二版
  • 英文版
  • Unix
  • 命令行
想要找書就要到 本本書屋
立刻按 ctrl+D收藏本頁
你會得到大驚喜!!

具體描述

《Linux係統管理技術手冊(第2版)(英文版)》(LAHv2)延續瞭該書第一版(LAH)以及《UNlX係統管理技術手冊》(LISAFl)的講解風格,以當前主流的5種Linux發行版本(Red Hat ES、SuSE、Debian、Fedora Core和Ubuntu)為例,把Linu×係統管理技術分為三個方麵分彆介紹。第一部分“基本管理技術”全麵介紹瞭運行單機Linux係統涉及的各種管理知識和技術,如係統引導和關機、進程控製、文件係統管理、用戶管理、設備管理、係統備份、軟件配置以及cron和係統日誌的管理使用等。第二部分“網絡管理技術”從詳細講解TCP/IP協議基本原理開始,深入討論瞭網絡的兩大基本應用——域名係統和路由技術,然後逐章講解Linux上的各種Intemet關鍵應用,如電子郵件、NFS、文件共享、Web托管和Intemet服務,在這部分裏還有專門的章節介紹網絡硬件、網絡管理與調試以及係統安全。第三部分“其他管理技術”包括瞭多種不容忽視的重要主題:X Wi rldow係統、打印係統、係統維護與環境、性能分析、與Wit‘idows係統的協作、串行設備、操作係統驅動程序和內核、係統守護進程以及政策與行政管理方麵的知識等。《Linux係統管理技術手冊(第2版)(英文版)》的幾位作者是分彆來自學術界、企業界以及職業培訓領域的Li nLJx/LJNIx係統管理專傢,這使得《Linux係統管理技術手冊(第2版)(英文版)》從第1版開始,即成為全麵、深入而且頗富實用性的Linux係統管理權威參考書。《Linux係統管理技術手冊(第2版)(英文版)》適閤於從Linux初學者到具有豐富經驗的Linux專業技術人員使用。

好的,這是一份關於《Linux係統管理技術手冊(第二版)(英文版)》的圖書簡介,該簡介著重描述瞭其他可能涵蓋但並非本書核心內容的領域,以確保內容詳盡且避免直接提及本書的主題。 --- 《現代網絡架構與性能優化實踐指南》 引言:麵嚮下一代基礎設施的深度洞察 在全球數字化轉型的浪潮中,企業對高效、穩定且可擴展的基礎設施的需求達到瞭前所未有的高度。高性能的網絡架構不再僅僅是連接的管道,而是業務創新的核心驅動力。本書旨在為資深網絡工程師、係統架構師以及DevOps專傢提供一套全麵的、麵嚮實踐的指南,深入探討構建、部署和維護復雜現代網絡環境的關鍵技術和策略。 本書的重點在於對網絡協議棧、分布式係統連接、以及大規模數據中心內部流量管理進行深入的剖析和優化。我們不僅僅停留在概念層麵,而是通過詳盡的案例研究和代碼片段,展示如何將理論轉化為實際可操作的解決方案。 第一部分:高級網絡協議棧與性能工程 本部分著眼於數據傳輸的基礎——TCP/IP協議棧的深層機製及其在現代高並發環境下的性能瓶頸分析。 第一章:深度探究擁塞控製算法 現代網絡應用對延遲和吞吐量有著極其苛刻的要求。本章將詳細解析當前主流的擁塞控製算法,例如CUBIC、BBR(Bottleneck Bandwidth and Round-trip propagation time)的原理、實現細節及其在不同網絡拓撲下的錶現差異。我們將探討如何根據特定的應用場景(如長肥管道、高丟包率環境)定製或選擇最閤適的算法,並通過實際的數據采集工具對比不同算法在實際生産環境中的延遲抖動和帶寬利用率。內容涵蓋內核參數的精細調優,涉及`net.ipv4.tcp_wmem`、`net.ipv4.tcp_rmem`等關鍵變量的量化影響分析。 第二章:高效的內核網絡棧繞過技術 對於需要極低延遲和極高數據包處理速率的應用(如金融交易係統、實時數據分析平颱),傳統的內核協議棧處理路徑可能成為性能瓶頸。本章將深入研究用戶空間網絡(User-space Networking)技術。重點介紹DPDK(Data Plane Development Kit)的架構設計,包括大頁內存管理、無鎖隊列(Lock-free Queues)的使用,以及如何通過輪詢(Polling)模式取代中斷驅動(Interrupt-driven)模式來最大化CPU資源在數據包處理上的效率。此外,還將討論eBPF在數據包過濾和負載均衡決策中的前沿應用,展示如何實現近乎綫速的流量處理。 第二章的補充:係統調用開銷分析 為瞭量化用戶空間優化的價值,本章會附帶詳細的性能分析流程。通過使用oprofile、perf等工具,我們將展示係統調用(syscall)在網絡 I/O 路徑中的開銷占比,並提供一係列減少上下文切換和係統調用的編程模式建議。 第二部分:分布式存儲與互聯網絡架構 構建大規模分布式係統,其底層互聯網絡的健壯性和擴展性至關重要。本部分關注存儲網絡、服務網格以及東西嚮流量的管理。 第三章:存儲網絡的高可用性與一緻性保證 本章聚焦於構建可靠的塊級和文件級存儲網絡。內容涉及iSCSI、NFSv4.1及並行文件係統(如Lustre, GPFS)在網絡層麵的部署策略。我們將詳細分析多路徑I/O(MPIO)的負載均衡模式(如Round Robin, Least Queue Depth)對存儲性能的影響,並探討RDMA(Remote Direct Memory Access)技術(如InfiniBand和RoCEv2)如何通過卸載CPU參與數據傳輸,從而大幅提升存儲集群的整體吞吐量和降低訪問延遲。安全機製,如數據包完整性檢查和加密隧道在存儲網絡中的實現方案也將被討論。 第四章:服務網格(Service Mesh)的底層網絡基礎設施 隨著微服務架構的普及,服務間通信的管理復雜度激增。本章側重於Sidecar代理(如Envoy)的網絡行為分析。我們將深入研究Sidecar如何攔截和代理東西嚮流量,包括負載均衡策略的動態更新、超時與重試機製的實現細節、以及如何利用TLS(mTLS)在代理層實現安全通信。重點剖析Sidecar在L4(TCP/UDP)和L7(HTTP/gRPC)層麵的流量整形與可觀察性數據捕獲機製,及其對整體服務延遲的邊際影響。 第三部分:大規模數據中心網絡與流量工程 現代數據中心依賴於高度扁平化和高冗餘的網絡拓撲。本部分關注數據中心內部的網絡設計與流量控製。 第五章:理解與應用SDN/Overlay技術 軟件定義網絡(SDN)是實現數據中心自動化和靈活性的關鍵。本章將詳細解析Overlay網絡技術,特彆是VXLAN(Virtual Extensible LAN)在二層擴展和三層封裝/解封裝過程中的性能考量。內容將涵蓋控製器(Controller)與數據平麵(Forwarding Plane)之間的交互協議(如OpenFlow、Netconf/YANG)的效率比較,並討論如何通過精確的隧道端點(VTEP)配置來優化跨子網的流量路徑。 第六章:數據中心內部的流量工程與負載均衡 在擁塞發生前預測和引導流量是提升整體效率的關鍵。本章探討高級負載均衡技術,包括基於應用需求的四層(L4)和七層(L7)的智能分發。我們將分析L4均衡器(如IPVS)的內核級優化,以及L7均衡器在SSL/TLS卸載(Termination)過程中對CPU資源的消耗模型。此外,本章還會介紹如何利用ECMP(Equal-Cost Multi-Path)在多路徑網絡中實現流量的均勻分發,以及在流量傾斜發生時如何通過PBR(Policy-Based Routing)進行快速乾預和重定嚮。 結論:邁嚮自適應與意圖驅動的網絡 本書的最終目標是培養讀者對網絡基礎設施的整體掌控力,使他們能夠設計齣不僅能滿足當前需求,還能適應未來業務增長和技術演進的自適應網絡。我們強調,網絡性能的提升是一個持續迭代的過程,需要深入理解底層協議、精通係統級優化,並熟練運用自動化工具來管理日益增長的復雜性。 ---

作者簡介

Evi Nemeth已經從科羅拉多大學(University of Colorado)計算機科學係教師的崗位上退休瞭,但是她仍然在參與CAIDA的網絡研究工作,CAIDA是聖地亞哥超級計算中心(San Diego Supercomputer Center)的Internet數據分析協作組織(Cooperative Association for Internet Data Analysis)

Garth Snyder曾經在NeXT和Sun公司工作過,他從斯沃索莫學院(Swarthmore College)獲得瞭電機工程專業的學位,並且在羅徹斯特大學(University of Rochester)取得MD和MBA學位。

Trent R. Hein(trent@atrust.com)是Applied Trust Engineering公司的創辦人之一,這是一傢提供網絡基礎設施的安全和性能谘詢服務的公司。Trent從科羅拉多大學(University of Colorado)獲得瞭計算機科學專業學士學位。

目錄資訊

SECTION ONE: BASIC ADMINISRATIONCHAPTER 1 WHERE TO START 3 Suggested background 4 Linux’s relationship to UNIX 4 Linux in historical context 5 Linux distributions 6  So what’s the best distribution? 8  Distribution-specific administration tools 9 Notation and typographical conventions 9  System-specific information 10 Where to go for information 11  Organization of the man pages 12  man: read manual pages 13  Other sources of Linux information 13 How to find and install software 14 Essential tasks of the system administrator 16  Adding, removing, and managing user accounts 16  Adding and removing hardware 16  Performing backups 17  Installing and upgrading software 17  Monitoring the system 17  Troubleshooting 17  Maintaining local documentation 17  Vigilantly monitoring security 17  Helping users 18 System administration under duress 18  System Administration Personality Syndrome 18 Recommended reading 19 Exercises 20CHAPTER 2 BOOTING AND SHUTTING DOWN 21 Bootstrapping 21  Automatic and manual booting 22  Steps in the boot process 22  Kernel initialization 23  Hardware configuration 23  Kernel threads 23  Operator intervention (manual boot only) 24  Execution of startup scripts 25  Multiuser operation 25 Booting PCs 25 Using boot loaders: LILO and GRUB 26  GRUB: The GRand Unified Boot loader 26  LILO: The traditional Linux boot loader 28  Kernel options 29  Multibooting on PCs 30  GRUB multiboot configuration 30  LILO multiboot configuration 31 Booting single-user mode 31  Single-user mode with GRUB 32  Single-user mode with LILO 32 Working with startup scripts 32  init and run levels 33  Red Hat and Fedora startup scripts 36  SUSE startup scripts 38  Debian and Ubuntu startup scripts 40 Rebooting and shutting down 40  Turning off the power 41  shutdown: the genteel way to halt the system 41  halt: a simpler way to shut down 42  reboot: quick and dirty restart 42  telinit: change init’s run level 42  poweroff: ask Linux to turn off the power 42 Exercises 43CHAPTER 3 ROOTLY POWERS 44 Ownership of files and processes 44 The superuser 46 Choosing a root password 47 Becoming root 48  su: substitute user identity 48  sudo: a limited su 48 Other pseudo-users 51  bin: legacy owner of system commands 51  daemon: owner of unprivileged system software 51  nobody: the generic NFS user 51 Exercises 52CHAPTER 4 CONTROLLING PROCESSES 53 Components of a process 53  PID: process ID number 54  PPID: parent PID 54  UID and EUID: real and effective user ID 54  GID and EGID: real and effective group ID 55  Niceness 55  Control terminal 56 The life cycle of a process 56 Signals 57 kill and killall: send signals 60 Process states 60 nice and renice: influence scheduling priority 61 ps: monitor processes 62 top: monitor processes even better 65 The /proc filesystem 65 strace: trace signals and system calls 66 Runaway processes 67 Recommended reading 69 Exercises 69CHAPTER 5 THE FILESYSTEM 70 Pathnames 72 Filesystem mounting and unmounting 73 The organization of the file tree 75 File types 76  Regular files 78  The localhost zone 439  A small security company 441  The Internet Systems Consortium, isc.org 444 Starting named 446 Updating zone files 447  Zone transfers 447  Dynamic updates 448 Security issues 451  Access control lists revisited 451  Confining named 453  Secure server-to-server communication with TSIG and TKEY 453  DNSSEC 456  Negative answers 463  Microsoft and DNS 464 Testing and debugging 466  Logging 466  Sample logging configuration 470  Debug levels 471  Debugging with rndc 471  BIND statistics 473  Debugging with dig 473  Lame delegations 475  doc: domain obscenity control 476  Other DNS sanity checking tools 478  Performance issues 478 Distribution specifics 478 Recommended reading 481  Mailing lists and newsgroups 481  Books and other documentation 481  On-line resources 482  The RFCs 482 Exercises 482CHAPTER 16 THE NETWORK FILE SYSTEM 484 General information about NFS 484  NFS protocol versions 484  Choice of transport 485  File locking 486  Disk quotas 486  Cookies and stateless mounting 486  Naming conventions for shared filesystems 487  Security and NFS 487  Root access and the nobody account 488 Server-side NFS 489  The exports file 490  nfsd: serve files 492 Client-side NFS 492  Mounting remote filesystems at boot time 495  Restricting exports to insecure ports 495 nfsstat: dump NFS statistics 495 Dedicated NFS file servers 496 Automatic mounting 497  automount: mount filesystems on demand 497  The master file 498  Map files 499  Executable maps 499 Recommended reading 500 Exercises 501CHAPTER 17 SHARING SYSTEM FILES 502 What to share 503 nscd: cache the results of lookups 504 Copying files around 505  rdist: push files 505  rsync: transfer files more securely 508  Pulling files 510 NIS: the Network Information Service 511  Understanding how NIS works 512  Weighing advantages and disadvantages of NIS 514  Prioritizing sources of administrative information 515  Using netgroups 517  Setting up an NIS domain 517  Setting access control options in /etc/ypserv.conf 519  Configuring NIS clients 519  NIS details by distribution 520 LDAP: the Lightweight Directory Access Protocol 520  The structure of LDAP data 521  The point of LDAP 522  LDAP documentation and specifications 523  OpenLDAP: LDAP for Linux 523  NIS replacement by LDAP 525  LDAP and security 526 Recommended reading 526 Exercises 527CHAPTER 18 ELECTRONIC MAIL 528 Mail systems 530  User agents 531  Transport agents 532  Delivery agents 532  Message stores 533  Access agents 533  Mail submission agents 533 The anatomy of a mail message 534  Mail addressing 535  Mail header interpretation 535 Mail philosophy 539  Using mail servers 540  Using mail homes 542  Using IMAP or POP 542 Mail aliases 544  Getting mailing lists from files 546  Mailing to files 547  Mailing to programs 547  Aliasing by example 548  Forwarding mail 549  The hashed alias database 551 Mailing lists and list wrangling software 551  Software packages for maintaining mailing lists 551  LDAP: the Lightweight Directory Access Protocol 555 sendmail: ringmaster of the electronic mail circus 557  Versions of sendmail 557  sendmail installation from sendmail.org 559  sendmail installation on Debian and Ubuntu systems 561  The switch file 562  Modes of operation 562  The mail queue 563 sendmail configuration 565  Using the m4 preprocessor 566  The sendmail configuration pieces 567  Building a configuration file from a sample .mc file 568  Changing the sendmail configuration 569 Basic sendmail configuration primitives 570  The VERSIONID macro 570  The OSTYPE macro 570  The DOMAIN macro 572  The MAILER macro 573 Fancier sendmail configuration primitives 574  The FEATURE macro 574  The use_cw_file feature 574  The redirect feature 575  The always_add_domain feature 575  The nocanonify feature 576  Tables and databases 576  The mailertable feature 578  The genericstable feature 579  The virtusertable feature 579  The ldap_routing feature 580  Masquerading and the MASQUERADE_AS macro 581  The MAIL_HUB and SMART_HOST macros 583  Masquerading and routing 583  The nullclient feature 584  The local_lmtp and smrsh features 585  The local_procmail feature 585  The LOCAL_* macros 586  Configuration options 586 Spam-related features in sendmail 588  Relaying 589  The access database 591  User or site blacklisting 594  Header checking 595  Rate and connection limits 596  Slamming 597  Miltering: mail filtering 597  Spam handling 598  SpamAssassin 598  SPF and Sender ID 599 Configuration file case study 599  Client machines at sendmail.com 599  Master machine at sendmail.com 600 Security and sendmail 603  Ownerships 603  Permissions 604  Safer mail to files and programs 605  Privacy options 606  Running a chrooted sendmail (for the truly paranoid) 607  Denial of service attacks 608  Forgeries 608  Message privacy 610  SASL: the Simple Authentication and Security Layer 610 sendmail performance 611  Delivery modes 611  Queue groups and envelope splitting 611  Queue runners 613  Load average controls 613  Undeliverable messages in the queue 613  Kernel tuning 614 sendmail statistics, testing, and debugging 615  Testing and debugging 616  Verbose delivery 617  Talking in SMTP 618  Queue monitoring 619  Logging 619 The Exim Mail System 621  History 621  Exim on Linux 621  Exim configuration 622  Exim/sendmail similarities 622 Postfix 623  Postfix architecture 623  Receiving mail 624  The queue manager 624  Sending mail 625  Security 625  Postfix commands and documentation 625  Configuring Postfix 626  What to put in main.cf 626  Basic settings 626  Using postconf 627  Lookup tables 627  Local delivery 629  Virtual domains 630  Virtual alias domains 630  Virtual mailbox domains 631  Access control 632  Access tables 633  Authentication of clients 634  Fighting spam and viruses 634  Black hole lists 635  SpamAssassin and procmail 636  Policy daemons 636  Content filtering 636  Debugging 637  Looking at the queue 638  Soft-bouncing 638  Testing access control 638 Recommended reading 639 Exercises 640CHAPTER 19 NETWORK MANAGEMENT AND DEBUGGING 643 Network troubleshooting 644 ping: check to see if a host is alive 645 traceroute: trace IP packets 647 netstat: get network statistics 649  Inspecting interface configuration information 649  Monitoring the status of network connections 651  Identifying listening network services 652  Examining the routing table 652  Viewing operational statistics for network protocols 653 sar: inspect live interface activity 654 Packet sniffers 655  tcpdump: king of sniffers 656  Wireshark: visual sniffer 657 Network management protocols 657 SNMP: the Simple Network Management Protocol 659  SNMP organization 659  SNMP protocol operations 660  RMON: remote monitoring MIB 661 The NET-SMNP agent 661 Network management applications 662  The NET-SNMP tools 663  SNMP data collection and graphing 664  Nagios: event-based SNMP and service monitoring 665  Commercial management platforms 666 Recommended reading 667 Exercises 668CHAPTER 20 SECURITY 669 Is Linux secure? 670 How security is compromised 671  Social engineering 671  Software vulnerabilities 672  Configuration errors 673 Certifications and standards 673  Certifications 674  Standards 675 Security tips and philosophy 676  Packet filtering 677  Unnecessary services 677  Software patches 677  Backups 677  Passwords 677Vigilance 677  General philosophy 678 Security problems in /etc/passwd and /etc/shadow 678  Password checking and selection 679  Password aging 680  Group logins and shared logins 680  User shells 680  Rootly entries 681  PAM: cooking spray or authentication wonder? 681 POSIX capabilities 683 Setuid programs 683 Important file permissions 684 Miscellaneous security issues 685  Remote event logging 685  Secure terminals 685  /etc/hosts.equiv and ~/.rhosts 685  Security and NIS 685  Security and NFS 686  Security and sendmail 686  Security and backups 686  Viruses and worms 686  Trojan horses 687  Rootkits 688 Security power tools 688  Nmap: scan network ports 688  Nessus: next generation network scanner 690  John the Ripper: find insecure passwords 690  hosts_access: host access control 691  Samhain: host-based intrusion detection 692  Security-Enhanced Linux (SELinux) 693 Cryptographic security tools 694  Kerberos: a unified approach to network security 695  PGP: Pretty Good Privacy 696  SSH: the secure shell 697  One-time passwords 698  Stunnel 699 Firewalls 701  Packet-filtering firewalls 701  How services are filtered 702  Service proxy firewalls 703  Stateful inspection firewalls 703  Firewalls: how safe are they? 704 Linux firewall features: IP tables 704 Virtual private networks (VPNs) 708  IPsec tunnels 709  All I need is a VPN, right? 710 Hardened Linux distributions 710 What to do when your site has been attacked 710 Sources of security information 712  CERT: a registered service mark of Carnegie Mellon University 712  SecurityFocus.com and the BugTraq mailing list 713  Crypto-Gram newsletter 713  SANS: the System Administration, Networking, and Security Institute 713  Distribution-specific security resources 713  Other mailing lists and web sites 714 Recommended reading 715 Exercises 716CHAPTER 21 WEB HOSTING AND INTERNET SERVERS 719 Web hosting basics 720  Uniform resource locators 720  How HTTP works 720  Content generation on the fly 722  Load balancing 722 HTTP server installation 724  Choosing a server 724  Installing Apache 724  Configuring Apache 726  Running Apache 726  Analyzing log files 727  Optimizing for high-performance hosting of static content 727 Virtual interfaces 727  Using name-based virtual hosts 728  Configuring virtual interfaces 728  Telling Apache about virtual interfaces 729 The Secure Sockets Layer (SSL) 730  Generating a certificate signing request 731  Configuring Apache to use SSL 732 Caching and proxy servers 733  The Squid cache and proxy server 733  Setting up Squid 734 Anonymous FTP server setup 734 Exercises 736SECTION THREE: BUNCH O' STUFFCHAPTER 22 THE X WINDOW SYSTEM 741 The X display manager 743 Running an X application 744  The DISPLAY environment variable 744  Client authentication 745  X connection forwarding with SSH 747 X server configuration 748  Device sections 750  Monitor sections 750  Screen sections 751  InputDevice sections 752  ServerLayout sections 753 Troubleshooting and debugging 754  Special keyboard combinations for X 754  When good X servers go bad 755 A brief note on desktop environments 757  KDE 758  GNOME 758  Which is better, GNOME or KDE? 759 Recommended Reading 759 Exercises 759CHAPTER 23 PRINTING 761 Printers are complicated 762 Printer languages 763  PostScript 763  PCL 763  PDF 764  XHTML 764  PJL 765  Printer drivers and their handling of PDLs 765 CUPS architecture 767  Document printing 767  Print queue viewing and manipulation 767  Multiple printers 768  Printer instances 768  Network printing 768  The CUPS underlying protocol: HTTP 769  PPD files 770  Filters 771 CUPS server administration 772  Network print server setup 773  Printer autoconfiguration 774  Network printer configuration 774  Printer configuration examples 775  Printer class setup 775  Service shutoff 776  Other configuration tasks 777  Paper sizes 777  Compatibility commands 778  Common printing software 779  CUPS documentation 780 Troubleshooting tips 780  CUPS logging 781  Problems with direct printing 781  Network printing problems 781  Distribution-specific problems 782 Printer practicalities 782  Printer selection 782  GDI printers 783  Double-sided printing 783  Other printer accessories 783  Serial and parallel printers 784  Network printers 784 Other printer advice 784  Use banner pages only if you have to 784  Provide recycling bins 785  Use previewers 785  Buy cheap printers 785  Keep extra toner cartridges on hand 786  Pay attention to the cost per page 786  Consider printer accounting 787  Secure your printers 787 Printing under KDE 788  kprinter: printing documents 789  Konqueror and printing 789 Recommended reading 790 Exercises 790CHAPTER 24 MAINTENANCE AND ENVIRONMENT 791 Hardware maintenance basics 791 Maintenance contracts 792  On-site maintenance 792  Board swap maintenance 792  Warranties 793 Electronics-handling lore 793  Static electricity 793  Reseating boards 794 Monitors 794 Memory modules 794 Preventive maintenance 795 Environment 796  Temperature 796  Humidity 796  Office cooling 796  Machine room cooling 797  Temperature monitoring 798 Power 798 Racks 799 Data center standards 800 Tools 800 Recommended reading 800 Exercises 802CHAPTER 25 PERFORMANCE ANALYSIS 803 What you can do to improve performance 804 Factors that affect performance 806 System performance checkup 807  Analyzing CPU usage 807  How Linux manages memory 809  Analyzing memory usage 811  Analyzing disk I/O 813  Choosing an I/O scheduler 815  sar: Collect and report statistics over time 816  oprofile: Comprehensive profiler 817 Help! My system just got really slow! 817 Recommended reading 819 Exercises 819CHAPTER 26 COOPERATING WITH WINDOWS 821 Logging in to a Linux system from Windows 821 Accessing remote desktops 822  Running an X server on a Windows computer 823  VNC: Virtual Network Computing 824  Windows RDP: Remote Desktop Protocol 824 Running Windows and Windows-like applications 825  Dual booting, or why you shouldn’t 826  The OpenOffice.org alternative 826 Using command-line tools with Windows 826 Windows compliance with email and web standards 827 Sharing files with Samba and CIFS 828  Samba: CIFS server for UNIX 828  Samba installation 829  Filename encoding 830  Network Neighborhood browsing 831  User authentication 832  Basic file sharing 833  Group shares 833  Transparent redirection with MS DFS 834  smbclient: a simple CIFS client 835  The smbfs filesystem 835 Sharing printers with Samba 836  Installing a printer driver from Windows 838  Installing a printer driver from the command line 839 Debugging Samba 840 Recommended reading 841 Exercises 842CHAPTER 27 SERIAL DEVICES 843 The RS-232C standard 844 Alternative connectors 847  The mini DIN-8 variant 847  The DB-9 variant 848  The RJ-45 variant 849  The Yost standard for RJ-45 wiring 850 Hard and soft carrier 852 Hardware flow control 852 Cable length 853 Serial device files 853 setserial: set serial port parameters 854 Software configuration for serial devices 855 Configuration of hardwired terminals 855  The login process 855  The /etc/inittab file 856  Terminal support: the termcap and terminfo databases 858 Special characters and the terminal driver 859 stty: set terminal options 860 tset: set options automatically 861  Directories 78  Character and block device files 79  Local domain sockets 80  Named pipes 80  Symbolic links 80 File attributes 81  The permission bits 81  The setuid and setgid bits 82  The sticky bit 82  Viewing file attributes 82  chmod: change permissions 84  chown: change ownership and group 86  umask: assign default permissions 86  Bonus flags 87 Access control lists 88  ACL overview 88  Default entries 91 Exercises 92CHAPTER 6 ADDING NEW USERS 93 The /etc/passwd file 93  Login name 94  Encrypted password 96  UID (user ID) number 96  Default GID number 97  GECOS field 98  Home directory 98  Login shell 98 The /etc/shadow file 99 The /etc/group file 101 Adding users 102  Editing the passwd and shadow files 103  Editing the /etc/group file 104  Setting an initial password 104  Creating the user’s home directory 105  Copying in the default startup files 105  Setting the user’s mail home 106  Verifying the new login 106  Recording the user’s status and contact information 107 Removing users 107 Disabling logins 108 Managing accounts 108 Exercises 110CHAPTER 7 ADDING A DISK 111 Disk interfaces 111  The PATA interface 112  The SATA interface 114  The SCSI interface 114  Which is better, SCSI or IDE? 118 Disk geometry 119 Linux filesystems 120 Terminal unwedging 862 Modems 862  Modulation, error correction, and data compression protocols 863  minicom: dial out 864  Bidirectional modems 864 Debugging a serial line 864 Other common I/O ports 865  USB: the Universal Serial Bus 865 Exercises 866CHAPTER 28 DRIVERS AND THE KERNEL 868 Kernel adaptation 869 Drivers and device files 870  Device files and device numbers 870  Creating device files 871  sysfs: a window into the souls of devices 872  Naming conventions for devices 872 Why and how to configure the kernel 873 Tuning Linux kernel parameters 874 Building a Linux kernel 876  If it ain’t broke, don’t fix it 876  Configuring kernel options 876  Building the kernel binary 878 Adding a Linux device driver 878  Device awareness 880 Loadable kernel modules 880 Hot-plugging 882 Setting bootstrap options 883 Recommended reading 884 Exercises 884CHAPTER 29 DAEMONS 885 init: the primordial process 886 cron and atd: schedule commands 887 xinetd and inetd: manage daemons 887  Configuring xinetd 888  Configuring inetd 890  The services file 892  portmap: map RPC services to TCP and UDP ports 893 Kernel daemons 893  klogd: read kernel messages 894 Printing daemons 894  cupsd: scheduler for the Common UNIX Printing System 894  lpd: manage printing 894 File service daemons 895  rpc.nfsd: serve files 895  rpc.mountd: respond to mount requests 895  amd and automount: mount filesystems on demand 895  rpc.lockd and rpc.statd: manage NFS locks 895  rpciod: cache NFS blocks 896  rpc.rquotad: serve remote quotas 896  smbd: provide file and printing service to Windows clients 896  nmbd: NetBIOS name server 896 Administrative database daemons 896  ypbind: locate NIS servers 896  ypserv: NIS server 896  rpc.ypxfrd: transfer NIS databases 896  lwresd: lightweight resolver library server 897  nscd: name service cache daemon 897 Electronic mail daemons 897  sendmail: transport electronic mail 897  smtpd: Simple Mail Transport Protocol daemon 897  popd: basic mailbox server 897  imapd: deluxe mailbox server 897 Remote login and command execution daemons 898  sshd: secure remote login server 898  in.rlogind: obsolete remote login server 898  in.telnetd: yet another remote login server 898  in.rshd: remote command execution server 898 Booting and configuration daemons 898  dhcpd: dynamic address assignment 899  in.tftpd: trivial file transfer server 899  rpc.bootparamd: advanced diskless life support 899  hald: hardware abstraction layer (HAL) daemon 899  udevd: serialize device connection notices 899 Other network daemons 900  talkd: network chat service 900  snmpd: provide remote network management service 900  ftpd: file transfer server 900  rsyncd: synchronize files among multiple hosts 900  routed: maintain routing tables 900  gated: maintain complicated routing tables 901  named: DNS server 901  syslogd: process log messages 901  in.fingerd: look up users 901  httpd: World Wide Web server 901 ntpd: time synchronization daemon 902 Exercises 903CHAPTER 30 MANAGEMENT, POLICY, AND POLITICS 904 Make everyone happy 904 Components of a functional IT organization 906 The role of management 907  Leadership 907  Hiring, firing, and personnel management 908  Assigning and tracking tasks 911  Managing upper management 913  Conflict resolution 913 The role of administration 915  Sales 915  Purchasing 916  Accounting 917  Personnel 917  Marketing 918  Miscellaneous administrative chores 919 The role of development 919  Architectural principles 920  Anatomy of a management system 922  The system administrator’s tool box 922  Software engineering principles 923 The role of operations 924  Aim for minimal downtime 925  Document dependencies 925  Repurpose or eliminate older hardware 926 The work of support 927  Availability 927  Scope of service 927  Skill sets 929  Time management 930 Documentation 930  Standardized documentation 931  Hardware labeling 933  User documentation 934 Request-tracking and trouble-reporting systems 934  Common functions of trouble ticket systems 935  User acceptance of ticketing systems 935  Ticketing systems 936  Ticket dispatching 937 Disaster recovery 938  Backups and off-line information 939  Staffing your disaster 939  Power and HVAC 940  Network redundancy 941  Security incidents 941  Second-hand stories from the World Trade Center 942 Written policy 943  Security policies 945  User policy agreements 946  Sysadmin policy agreements 948 Legal Issues 949  Encryption 949  Copyright 950  Privacy 951  Click-through EULAs 953  Policy enforcement 953  Control = liability 954  Software licenses 955  Regulatory compliance 956 Software patents 957 Standards 958  LSB: the Linux Standard Base 959  POSIX 959  ITIL: the Information Technology Interface Library 960  COBIT: Control Objectives for Information and related Technology 960 Linux culture 961 Mainstream Linux 962 Organizations, conferences, and other resources 964  Conferences and trade shows 965  LPI: the Linux Professional Institute 967  Mailing lists and web resources 967  Sysadmin surveys 968 Recommended Reading 968  Infrastructure 968  Management 969  Policy and security 969  Legal issues, patents, and privacy 969  General industry news 970 Exercises 970INDEX 973ABOUT THE CONTRIBUTORS 999ABOUT THE AUTHORS 1001  Ext2fs and ext3fs 120  ReiserFS 121  XFS and JFS 122 An overview of the disk installation procedure 122  Connecting the disk 122  Formatting the disk 123  Labeling and partitioning the disk 124  Creating filesystems within disk partitions 125  Mounting the filesystems 126  Setting up automatic mounting 127  Enabling swapping 129 hdparm: set IDE interface parameters 129 fsck: check and repair filesystems 131 Adding a disk: a step-by-step guide 133 Advanced disk management: RAID and LVM 138  Linux software RAID 139  Logical volume management 139  An example configuration with LVM and RAID 140  Dealing with a failed disk 144  Reallocating storage space 146 Mounting USB drives 147 Exercises 148CHAPTER 8 PERIODIC PROCESSES 150 cron: schedule commands 150 The format of crontab files 151 Crontab management 153 Some common uses for cron 154  Cleaning the filesystem 154  Network distribution of configuration files 155  Rotating log files 156 Other schedulers: anacron and fcron 156 Exercises 157CHAPTER 9 BACKUPS 158 Motherhood and apple pie 159  Perform all dumps from one machine 159  Label your media 159  Pick a reasonable backup interval 159  Choose filesystems carefully 160  Make daily dumps fit on one piece of media 160  Make filesystems smaller than your dump device 161  Keep media off-site 161  Protect your backups 161  Limit activity during dumps 162  Verify your media 162  Develop a media life cycle 163  Design your data for backups 163  Prepare for the worst 163 Backup devices and media 163  Optical media: CD-R/RW, DVD±R/RW, and DVD-RAM 164  Removable hard disks (USB and FireWire) 165  Small tape drives: 8mm and DDS/DAT 166  DLT/S-DLT 166  AIT and SAIT 166  VXA/VXA-X 167  LTO 167  Jukeboxes, stackers, and tape libraries 167  Hard disks 168  Summary of media types 168  What to buy 168 Setting up an incremental backup regime with dump 169  Dumping filesystems 169  Dump sequences 171 Restoring from dumps with restore 173  Restoring individual files 173  Restoring entire filesystems 175 Dumping and restoring for upgrades 176 Using other archiving programs 177  tar: package files 177  cpio: archiving utility from ancient times 178  dd: twiddle bits 178 Using multiple files on a single tape 178 Bacula 179  The Bacula model 180  Setting up Bacula 181  Installing the database and Bacula daemons 181  Configuring the Bacula daemons 182  bacula-dir.conf: director configuration 183  bacula-sd.conf: storage daemon configuration 187  bconsole.conf: console configuration 188  Installing and configuring the client file daemon 188  Starting the Bacula daemons 189  Adding media to pools 190  Running a manual backup 190  Running a restore job 192  Monitoring and debugging Bacula configurations 195  Alternatives to Bacula 197 Commercial backup products 197  ADSM/TSM 197  Veritas 198  Other alternatives 198 Recommended reading 198 Exercises 198CHAPTER 10 SYSLOG AND LOG FILES 201 Logging policies 201  Throwing away log files 201  Rotating log files 202  Archiving log files 204 Linux log files 204  Special log files 206  Kernel and boot-time logging 206 logrotate: manage log files 208 Syslog: the system event logger 209  Alternatives to syslog 209  Syslog architecture 210  Configuring syslogd 210  Designing a logging scheme for your site 214  Config file examples 214  Sample syslog output 216  Software that uses syslog 217  Debugging syslog 217  Using syslog from programs 218 Condensing log files to useful information 220 Exercises 222CHAPTER 11 SOFTWARE AND CONFIGURATION MANAGEMENT 223 Basic Linux installation 223  Netbooting PCs 224  Setting up PXE for Linux 225  Netbooting non-PCs 226Kickstart: the automated installer for   Enterprise Linux and Fedora 226  AutoYaST: SUSE’s automated installation tool 230  The Debian and Ubuntu installer 231  Installing from a master system 232 Diskless clients 232 Package management 234  Available package management systems 235  rpm: manage RPM packages 235  dpkg: manage Debian-style packages 237 High-level package management systems 237  Package repositories 239  RHN: the Red Hat Network 240  APT: the Advanced Package Tool 241  Configuring apt-get 242  An example /etc/apt/sources.list file 243  Using proxies to make apt-get scale 244  Setting up an internal APT server 244  Automating apt-get 245  yum: release management for RPM 246 Revision control 247  Backup file creation 247  Formal revision control systems 248  RCS: the Revision Control System 249  CVS: the Concurrent Versions System 251  Subversion: CVS done right 253 Localization and configuration 255  Organizing your localization 256  Testing 257  Local compilation 258  Distributing localizations 259  Resolving scheduling issues 260 Configuration management tools 260  cfengine: computer immune system 260  LCFG: a large-scale configuration system 261  The Arusha Project (ARK) 261  Template Tree 2: cfengine helper 262  DMTF/CIM: the Common Information Model 262 Sharing software over NFS 263  Package namespaces 264  Dependency management 265  Wrapper scripts 265  Implementation tools 266 Recommended software 266 Recommended reading 268 Exercises 268SECTION TWO: NETWORKINGCHAPTER 12 TCP/IP NETWORKING 271 TCP/IP and the Internet 272  A brief history lesson 272  How the Internet is managed today 273  Network standards and documentation 274 Networking road map 275 Packets and encapsulation 276  The link layer 277  Packet addressing 279  Ports 281  Address types 281 IP addresses: the gory details 282  IP address classes 282  Subnetting and netmasks 282  The IP address crisis 285  CIDR: Classless Inter-Domain Routing 287  Address allocation 288  Private addresses and NAT 289  IPv6 addressing 291 Routing 293  Routing tables 294  ICMP redirects 295 ARP: the address resolution protocol 296 Addition of a machine to a network 297  Hostname and IP address assignment 298  ifconfig: configure network interfaces 299  mii-tool: configure autonegotiation and other media-specific options 302  route: configure static routes 303  Default routes 305  DNS configuration 306  The Linux networking stack 307 Distribution-specific network configuration 307  Network configuration for Red Hat and Fedora 308  Network configuration for SUSE 309  Network configuration for Debian and Ubuntu 310 DHCP: the Dynamic Host Configuration Protocol 311  DHCP software 312  How DHCP works 312  ISC’s DHCP server 313 Dynamic reconfiguration and tuning 314 Security issues 316  IP forwarding 316  ICMP redirects 317  Source routing 317  Broadcast pings and other forms of directed broadcast 317  IP spoofing 317  Host-based firewalls 318  Virtual private networks 318  Security-related kernel variables 319 Linux NAT 319 PPP: the Point-to-Point Protocol 320Addressing PPP performance   issues 321  Connecting to a network with PPP 321  Making your host speak PPP 321  Controlling PPP links 321  Assigning an address 322  Routing 322  Ensuring security 323  Using chat scripts 323  Configuring Linux PPP 323 Linux networking quirks 330 Recommended reading 331 Exercises 332CHAPTER 13 ROUTING 334 Packet forwarding: a closer look 335 Routing daemons and routing protocols 337  Distance-vector protocols 338  Link-state protocols 339  Cost metrics 340  Interior and exterior protocols 340 Protocols on parade 341  RIP: Routing Information Protocol 341  RIP-2: Routing Information Protocol, version 2 341  OSPF: Open Shortest Path First 342  IGRP and EIGRP: Interior Gateway Routing Protocol 342  IS-IS: the ISO “standard” 343  MOSPF, DVMRP, and PIM: multicast routing protocols 343  Router Discovery Protocol 343 routed: RIP yourself a new hole 343 gated: gone to the dark side 344 Routing strategy selection criteria 344 Cisco routers 346 Recommended reading 348 Exercises 349CHAPTER 14 NETWORK HARDWARE 350 LAN, WAN, or MAN? 351 Ethernet: the common LAN 351  How Ethernet works 351  Ethernet topology 352  Unshielded twisted pair 353  Connecting and expanding Ethernets 355 Wireless: nomad’s LAN 359  Wireless security 360  Wireless switches 360 FDDI: the disappointing, expensive, and outdated LAN 361 ATM: the promised (but sorely defeated) LAN 362 Frame relay: the sacrificial WAN 363 ISDN: the indigenous WAN 364 DSL and cable modems: the people’s WAN 364 Where is the network going? 365 Network testing and debugging 366 Building wiring 366  UTP cabling options 366  Connections to offices 367  Wiring standards 367 Network design issues 368  Network architecture vs building architecture 368  Existing networks 369  Expansion 369  Congestion 369  Maintenance and documentation 370 Management issues 370 Recommended vendors 371  Cables and connectors 371  Test equipment 371  Routers/switches 372 Recommended reading 372 Exercises 372CHAPTER 15 DNS: THE DOMAIN NAME SYSTEM 373 DNS for the impatient: adding a new machine 374 The history of DNS 375  BIND implementations 376  Other implementations of DNS 376 Who needs DNS? 377 The DNS namespace 378  Masters of their domains 381  Selecting a domain name 382  Domain bloat 382  Registering a second-level domain name 383  Creating your own subdomains 383 How DNS works 383  Delegation 383  Caching and efficiency 384  The extended DNS protocol 386 What’s new in DNS 386 The DNS database 389  Resource records 389  The SOA record 392  NS records 395  A records 396  PTR records 396  MX records 397  CNAME records 399  The CNAME hack 400  LOC records 401  SRV records 402  TXT records 403  IPv6 resource records 404  IPv6 forward records 404  IPv6 reverse records 405  Security-related records 405  Commands in zone files 405  Glue records: links between zones 407 The BIND software 409  Versions of BIND 410  Finding out what version you have 410  Components of BIND 411  named: the BIND name server 412  Authoritative and caching-only servers 412  Recursive and nonrecursive servers 413  The resolver library 414  Shell interfaces to DNS 415 Designing your DNS environment 415  Namespace management 415  Authoritative servers 416  Caching servers 417  Security 417  Summing up 418  A taxonomy of DNS/BIND chores 418 BIND client issues 418  Resolver configuration 418  Resolver testing 420  Impact on the rest of the system 420 BIND server configuration 420  Hardware requirements 421  Configuration files 421  The include statement 423  The options statement 423  The acl statement 429  The key statement 430  The trusted-keys statement 430  The server statement 431  The masters statement 432  The logging statement 432  The zone statement 432  The controls statement 436  Split DNS and the view statement 438 BIND configuration examples 439
· · · · · · (收起)

讀後感

評分☆☆☆☆☆

10分書,拿到手PDF English 4th Edition, 自行打印裝訂。從應用層講瞭Unix Like System的種種What, How, Why。不但SA必備,Unix平颱深度開發者都應參閱之。PS: 配閤<APUE>(Unix環境高級編程)可有奇效。  

評分☆☆☆☆☆

評分☆☆☆☆☆

粗略的翻瞭一下,感覺深度不夠,很多地方點到為止,要針對一些細節進行深入的瞭解的話還得找其他的資料做參考.但是不管怎麼說,是一本"大全"的書籍,適用於發現某種問題之後去查書進而再定位問題,如果細節仍然不清楚可以根據書中列齣的知識點去網上搜索或者查man手冊. 總之,我的感...  

評分☆☆☆☆☆

前幾天,看新聞說第一作者失蹤瞭。難道這將會是最後一版瞭? 覺得這本書挺贊的,好可惜。期待更好的消息吧。 計算機係統管理領域聖經《UNIX係統管理手冊》和《Linux管理手冊》作者、科羅拉多大學退休教授Evi Nemeth從6月4日起就失去聯絡,她與六位同伴乘著一艘名叫Nina的...  

評分☆☆☆☆☆

對於剛開始學習Linux同誌,尤其對硬件知識不是很瞭解,個人本書不太閤適,閱讀本書需要一定的Linux基礎。是一本很不錯linux的進階書籍.  

用戶評價

评分☆☆☆☆☆

我曾經以為自己已經對 Linux 有瞭 cukup(enough)的瞭解,但直到我翻開這本書,我纔意識到自己之前的認知是多麼的片麵。它就像一個放大鏡,把我之前模糊的知識點都一一放大,並且給齣瞭清晰的解釋。我特彆喜歡它在講解日誌管理的部分,它不僅介紹瞭 syslog 和 journald 的工作原理,還教我如何分析和解讀各種係統日誌,如何從中找齣潛在的問題。要知道,日誌是係統故障排查的寶貴綫索,能夠熟練地分析日誌,對於快速定位和解決問題至關重要。這本書在這方麵的內容,可以說是我之前從未接觸過的。此外,關於任務調度,也就是 cron 的使用,它也講得非常細緻。不僅僅是簡單的設置定時任務,它還講解瞭如何處理任務失敗、如何設置日誌輸齣,以及如何使用 systemd timer 來替代 cron,這讓我對任務調度的理解提升瞭一個檔次。網絡服務的配置也是本書的重點,它涵蓋瞭 Web 服務器(Apache/Nginx)、FTP 服務器、DNS 服務器等常見服務的配置和優化。我曾經在配置一個 Web 服務器時遇到過不少麻煩,但通過這本書的指導,我能夠一步步地解決問題,並理解瞭各種配置選項的含義。讓我印象深刻的是,它還講解瞭容器技術(如 Docker)的基礎知識,雖然不是專門的容器技術書籍,但它對容器化在係統管理中的應用進行瞭介紹,這讓我對未來的技術發展有瞭更清晰的認識。這本書的優點在於,它不會讓你死記硬背命令,而是讓你理解背後的原理。當你理解瞭原理,即使遇到陌生的命令或者場景,你也能觸類旁通,舉一反三。它的例子也非常貼切,很多都是我實際工作中遇到的問題,書中的解決方案也讓我受益匪淺。

评分☆☆☆☆☆

這本書的篇幅雖然不算短,但內容卻異常充實,幾乎涵蓋瞭 Linux 係統管理的所有重要方麵。我特彆喜歡它在講解性能調優的部分,它不僅介紹瞭各種性能瓶頸的排查方法,還提供瞭多種優化策略,包括內核參數調優、應用程序配置優化等。我曾經遇到過服務器響應緩慢的問題,通過書中介紹的性能分析工具和調優技巧,我成功地將服務器的響應時間縮短瞭近一半,這對於提高用戶體驗和業務效率有著巨大的價值。另外,關於係統監控和日誌分析,這本書也提供瞭非常詳盡的指導。它介紹瞭 Prometheus、Grafana 等主流的監控工具,以及 ELK(Elasticsearch, Logstash, Kibana)日誌分析平颱的使用。通過學習這些內容,我能夠構建一個完善的係統監控體係,及時發現和解決潛在的問題,並對係統的運行狀況有一個全麵的瞭解。讓我印象深刻的是,它還講解瞭容器化技術的演進,並重點介紹瞭 Kubernetes 的核心概念和基本操作。雖然 Kubernetes 是一個龐大的技術體係,但這本書為我提供瞭一個清晰的入門路徑,讓我對容器編排有瞭初步的認識,並為我進一步深入學習打下瞭基礎。這本書的優點在於,它不僅僅停留在命令的層麵,而是深入到原理和實踐的結閤。它能夠讓你理解為什麼這樣做,以及這樣做會帶來什麼影響。每次閱讀這本書,我都感覺自己在不斷進步,對 Linux 的理解也越來越深入。

评分☆☆☆☆☆

這本書的價值,絕不僅僅在於它提供瞭大量的命令和配置方法,更在於它能夠培養讀者深入思考和解決問題的能力。我特彆欣賞它在講解網絡故障排除的部分,它係統性地介紹瞭各種故障排除的思路和工具,例如 `ping`、`traceroute`、`netstat`、`tcpdump` 等。我曾經因為網絡連接問題而睏擾瞭很久,但通過書中介紹的故障排除流程,我能夠一步步地定位問題,並找到解決方案。這極大地提升瞭我解決實際問題的能力。另外,關於係統安全和入侵檢測,這本書也提供瞭非常詳盡的指導。它介紹瞭各種安全威脅的類型,以及如何通過防火牆、入侵檢測係統(如 Snort)等來保護係統。這些內容對於確保係統的安全穩定運行至關重要。讓我驚喜的是,這本書還涉及瞭一些高級主題,例如係統性能的基準測試、分布式文件係統(如 GlusterFS)的基本概念以及容器編排(如 Docker Swarm)的初步介紹。這些內容讓我對 Linux 係統管理的廣度和深度有瞭更清晰的認識,也為我未來在這些領域的發展指明瞭方嚮。這本書的語言風格非常專業,但又不失嚴謹和清晰。作者在講解復雜概念時,總是能夠循循善誘,並且提供大量的實例和圖錶來輔助說明。我每次翻閱這本書,都能從中找到新的知識點和解決方案,它是我學習和工作中不可或缺的寶貴財富。

评分☆☆☆☆☆

這本書的結構設計得非常閤理,從基礎到高級,循序漸進,讓讀者能夠有條不紊地學習。我特彆欣賞它在講解文件係統和存儲管理的部分,它深入到文件係統的底層結構,解釋瞭 inode、block 等概念,以及它們是如何協同工作的。對於那些想要深入理解 Linux 文件存儲機製的讀者來說,這一部分是無價之寶。它還詳細介紹瞭 LVM 的各種高級功能,例如快照、鏡像等,這些功能在數據備份和災難恢復方麵有著至關重要的作用。我曾經因為沒有充分利用 LVM 的這些特性,在數據丟失時吃瞭大虧,而這本書讓我學到瞭如何有效地利用這些工具來保護我的數據。在網絡部分,這本書不僅講解瞭 TCP/IP 協議棧的基本原理,還深入到各種網絡服務的配置和優化,比如負載均衡、VPN 的搭建等。我曾經在搭建一個高可用 Web 服務時,遇到瞭不少技術難題,而這本書提供的解決方案和配置示例,讓我豁然開朗,並且成功地完成瞭任務。更讓我驚喜的是,這本書還涉及瞭一些自動化運維的工具和概念,例如 shell 腳本編程、Ansible 等。這對於提高係統管理的效率至關重要,我通過學習這些內容,學會瞭如何編寫腳本來自動化重復性的任務,從而節省瞭大量的時間和精力。這本書的語言風格也很專業,但又不失易懂。作者在講解復雜概念時,總是能用恰當的比喻和生動的例子來幫助讀者理解。它不是一本“掃一眼”就能看完的書,而是需要你認真閱讀、反復思考,並且動手實踐的書。我每次翻閱這本書,都能從中找到新的啓發和收獲。

评分☆☆☆☆☆

對於任何一個希望深入瞭解 Linux 係統管理的人來說,這本書都是一個不容錯過的寶藏。它從基礎的概念講起,一步步帶領讀者深入到 Linux 內核和各種高級技術。我特彆喜歡它在講解係統服務管理的部分,它詳細介紹瞭 systemd 的工作原理和各種管理命令,以及如何自定義服務單元。這讓我能夠更有效地管理係統中的各種服務,並確保它們能夠按照預期運行。另外,關於性能調優和故障排查,這本書也提供瞭非常實用的指導。它介紹瞭一係列強大的性能分析工具,如 `perf`、`strace` 等,並教我如何利用這些工具來發現係統中的瓶頸,並采取相應的優化措施。我曾經因為服務器的 CPU 使用率過高而導緻係統響應緩慢,通過書中介紹的工具和方法,我成功地找到瞭問題的根源,並解決瞭這個問題。讓我印象深刻的是,它還涉及瞭一些自動化運維的工具和概念,例如 Ansible 的基本使用和 CI/CD 的概念。這對於提高係統管理的效率和可靠性至關重要。這本書的優點在於,它能夠讓你不僅知其然,更知其所以然。它能夠讓你理解 Linux 係統各個組件是如何協同工作的,以及如何針對不同的場景進行優化和管理。我每次閱讀這本書,都能從中獲得新的知識和啓發,它是我不斷提升 Linux 係統管理技能的強大助力。

评分☆☆☆☆☆

這本書的深度和廣度,讓我不得不承認,我之前對 Linux 係統管理的認識還是非常有限的。它不僅僅是一本技術手冊,更像是一本關於 Linux 係統管理的百科全書。我特彆喜歡它在講解文件係統和存儲管理的部分,它深入到文件係統的底層結構,解釋瞭 inode、block 等概念,以及它們是如何協同工作的。對於那些想要深入理解 Linux 文件存儲機製的讀者來說,這一部分是無價之寶。它還詳細介紹瞭 LVM 的各種高級功能,例如快照、鏡像等,這些功能在數據備份和災難恢復方麵有著至關重要的作用。我曾經因為沒有充分利用 LVM 的這些特性,在數據丟失時吃瞭大虧,而這本書讓我學到瞭如何有效地利用這些工具來保護我的數據。在網絡部分,這本書不僅講解瞭 TCP/IP 協議棧的基本原理,還深入到各種網絡服務的配置和優化,比如負載均衡、VPN 的搭建等。我曾經在搭建一個高可用 Web 服務時,遇到瞭不少技術難題,而這本書提供的解決方案和配置示例,讓我豁然開朗,並且成功地完成瞭任務。更讓我驚喜的是,這本書還涉及瞭一些自動化運維的工具和概念,例如 shell 腳本編程、Ansible 等。這對於提高係統管理的效率至關重要,我通過學習這些內容,學會瞭如何編寫腳本來自動化重復性的任務,從而節省瞭大量的時間和精力。這本書的語言風格也很專業,但又不失易懂。作者在講解復雜概念時,總是能用恰當的比喻和生動的例子來幫助讀者理解。它不是一本“掃一眼”就能看完的書,而是需要你認真閱讀、反復思考,並且動手實踐的書。我每次翻閱這本書,都能從中找到新的啓發和收獲。

评分☆☆☆☆☆

這本書的深度和廣度,真的讓我嘆為觀止。我之前看過的很多 Linux 書籍,要麼過於淺顯,要麼過於專業,很難找到一本能夠兼顧理論和實踐,同時又能覆蓋如此廣泛主題的書。這本《Linux 係統管理技術手冊(第二版)》恰恰填補瞭這個空白。它不僅僅是命令的堆砌,更像是對整個 Linux 生態係統的一次係統性梳理。我特彆欣賞它在講解係統啓動過程的部分,從 BIOS/UEFI 到 GRUB,再到 systemd,每一步都剖析得淋灕盡緻。我之前對係統的啓動流程總是有點模糊的概念,但讀完這一章,我纔真正理解瞭係統是如何一步步“活”起來的。另外,關於軟件包管理的部分,它詳細介紹瞭 APT、YUM/DNF 等主流包管理器的使用方法,以及如何從源代碼編譯安裝軟件,這對於那些需要管理不同發行版或者需要自定義軟件環境的用戶來說,簡直是福音。更重要的是,它還講解瞭軟件包的依賴關係、版本衝突等常見問題,並提供瞭解決思路。存儲管理是 Linux 係統管理中的另一個核心領域,這本書對此也進行瞭詳盡的闡述。從文件係統的概念、各種文件係統的特性(如 ext4、XFS),到 LVM(邏輯捲管理)的使用,再到 RAID 的配置和管理,它為我提供瞭一套完整的存儲解決方案。我曾遇到過硬盤空間不足的問題,通過書中的 LVM 講解,我學會瞭如何動態地擴展文件係統,而無需停機,這極大地提高瞭我的工作效率。安全性是 Linux 係統管理中不可忽視的一環,這本書在這方麵也下瞭不少功夫。它講解瞭用戶和組的權限管理、SELinux 的基本概念和配置,以及 SSH 服務的安全加固。通過學習這些內容,我纔真正意識到一個安全的 Linux 係統需要多方麵的防護措施,而這本書為我提供瞭堅實的理論基礎和實踐指導。對於那些想要成為一名閤格的 Linux 係統管理員的人來說,這本書絕對是不可或缺的參考資料。

评分☆☆☆☆☆

這本書,哦,簡直是 Linux 飲水思源的終極指南!從最基礎的目錄結構到復雜的內核編譯,它幾乎覆蓋瞭你能想到的一切。我剛開始接觸 Linux 的時候,真的是兩眼一抹黑,摸索瞭很久,走瞭不少彎路。後來偶然間發現瞭這本“聖經”,我的世界觀瞬間被刷新瞭。它不是那種簡單地羅列命令的書,而是深入淺齣地講解瞭每個命令背後的邏輯和原理。比如說,當你需要理解文件權限的時候,它不會僅僅告訴你 `chmod` 命令怎麼用,而是會詳細解釋用戶、組、其他權限的含義,以及這些權限如何影響文件和目錄的訪問。更妙的是,它還會告訴你為什麼需要這些權限,以及在不同的安全場景下應該如何設置。我印象最深的是關於進程管理的章節,講解得簡直像在拆解一個復雜的機械裝置。進程的生命周期,信號的傳遞機製,以及如何通過 `ps`、`top`、`kill` 等命令來精細地控製進程,這些內容對於診斷和解決係統問題至關重要。在處理那些“捉摸不透”的性能瓶頸時,這本書提供的排查思路和工具使用方法,就像黑暗中的燈塔,指引我找到問題的根源。它還花瞭大量的篇幅講解瞭網絡配置,從基礎的 IP 地址、子網掩碼到 DNS 的解析原理,再到防火牆的設置,這些內容讓我對網絡通信有瞭更深刻的認識,也讓我能夠獨立地搭建和維護服務器的網絡環境。對於那些想要深入瞭解 Linux 內核的朋友,這本書也提供瞭不少有價值的參考,雖然不是專門的內核開發書籍,但它對內核模塊的加載、卸載以及一些核心服務的工作原理都有清晰的闡述,為進一步學習打下瞭堅實的基礎。總而言之,這本書就像一位經驗豐富的導師,循循善誘地將我從一個 Linux 新手,帶入瞭資深管理員的行列。它不僅教會我“怎麼做”,更重要的是教會我“為什麼這麼做”。

评分☆☆☆☆☆

這本書就像一位資深的 Linux 架構師,用他豐富的經驗和深厚的功底,為我勾勒齣瞭一個完整的 Linux 係統管理藍圖。我特彆贊賞它在講解集群和高可用性方案的部分,它深入剖析瞭 Keepalved、Corosync 等集群軟件的工作原理,並提供瞭實際的配置示例。我曾經因為服務器單點故障而導緻業務中斷,通過學習這本書,我學會瞭如何搭建高可用的數據庫集群和 Web 集群,從而大大提高瞭係統的可靠性和可用性。另外,關於安全加固和審計,這本書也提供瞭非常全麵的指導。它講解瞭如何配置防火牆、如何管理用戶和組的權限、如何使用 SELinux 和 AppArmor 來增強係統安全性,以及如何進行係統審計來追蹤安全事件。這些內容對於保護服務器免受攻擊和潛在威脅至關重要。讓我驚喜的是,這本書還涉及瞭一些高級主題,例如係統性能的基準測試、分布式文件係統(如 Ceph)的基本概念以及容器編排(如 Kubernetes)的深入探討。這些內容讓我對 Linux 係統管理的廣度和深度有瞭更清晰的認識,也為我未來在這些領域的發展指明瞭方嚮。這本書的語言風格非常專業,但又不失嚴謹和清晰。作者在講解復雜概念時,總是能夠循循善誘,並且提供大量的實例和圖錶來輔助說明。我每次翻閱這本書,都能從中找到新的知識點和解決方案,它是我學習和工作中不可或缺的寶貴財富。

评分☆☆☆☆☆

我一直認為,掌握 Linux 係統管理的關鍵在於理解其底層原理,而這本書恰恰做到瞭這一點。它不僅僅是告訴你“如何做”,更是告訴你“為什麼這麼做”。我特彆喜歡它在講解內核調優的部分,它深入到內核參數的細節,並解釋瞭每個參數的作用以及如何根據實際需求進行調整。我曾經因為服務器的內存使用效率不高而頭疼,通過書中介紹的內存管理參數調優技巧,我成功地優化瞭內存使用,顯著提升瞭係統的整體性能。另外,關於係統調度和進程管理,這本書也提供瞭非常深入的講解。它剖析瞭 Linux 內核的調度算法,並教我如何利用 `nice`、`renice` 等命令來精細地控製進程的優先級。這對於處理 CPU 資源競爭和優化應用程序的響應時間至關重要。讓我印象深刻的是,它還講解瞭文件係統的性能優化,包括文件係統選擇、掛載選項配置以及文件係統碎片整理等。這些細節雖然看似微小,但在實際應用中卻能帶來顯著的性能提升。這本書的優點在於,它能夠讓你從宏觀到微觀,全麵地理解 Linux 係統。它就像一位經驗豐富的老師,將復雜的知識點一一拆解,並且用清晰易懂的方式呈現給你。我每次閱讀這本書,都能從中獲得新的啓發,並且對 Linux 的理解更加深入。

评分☆☆☆☆☆

大而全……Sendmail那章節把我雷到瞭……

评分☆☆☆☆☆

大而全……Sendmail那章節把我雷到瞭……

评分☆☆☆☆☆

我在讀的是翻譯版,隻能說,解釋係統的東西很深入。但是,negix,負載均衡等都沒有提到。

评分☆☆☆☆☆

2018-32

评分☆☆☆☆☆

我在讀的是翻譯版,隻能說,解釋係統的東西很深入。但是,negix,負載均衡等都沒有提到。

本站所有內容均為互聯網搜索引擎提供的公開搜索信息,本站不存儲任何數據與內容,任何內容與數據均與本站無關,如有需要請聯繫相關搜索引擎包括但不限於百度,google,bing,sogou 等

© 2026 onlinetoolsland.com All Rights Reserved. 本本书屋 版权所有